
Rethinking enterprise security: from access control to risk intelligence
April 14, 20267 min readBy Techbanq Access Governance Practice
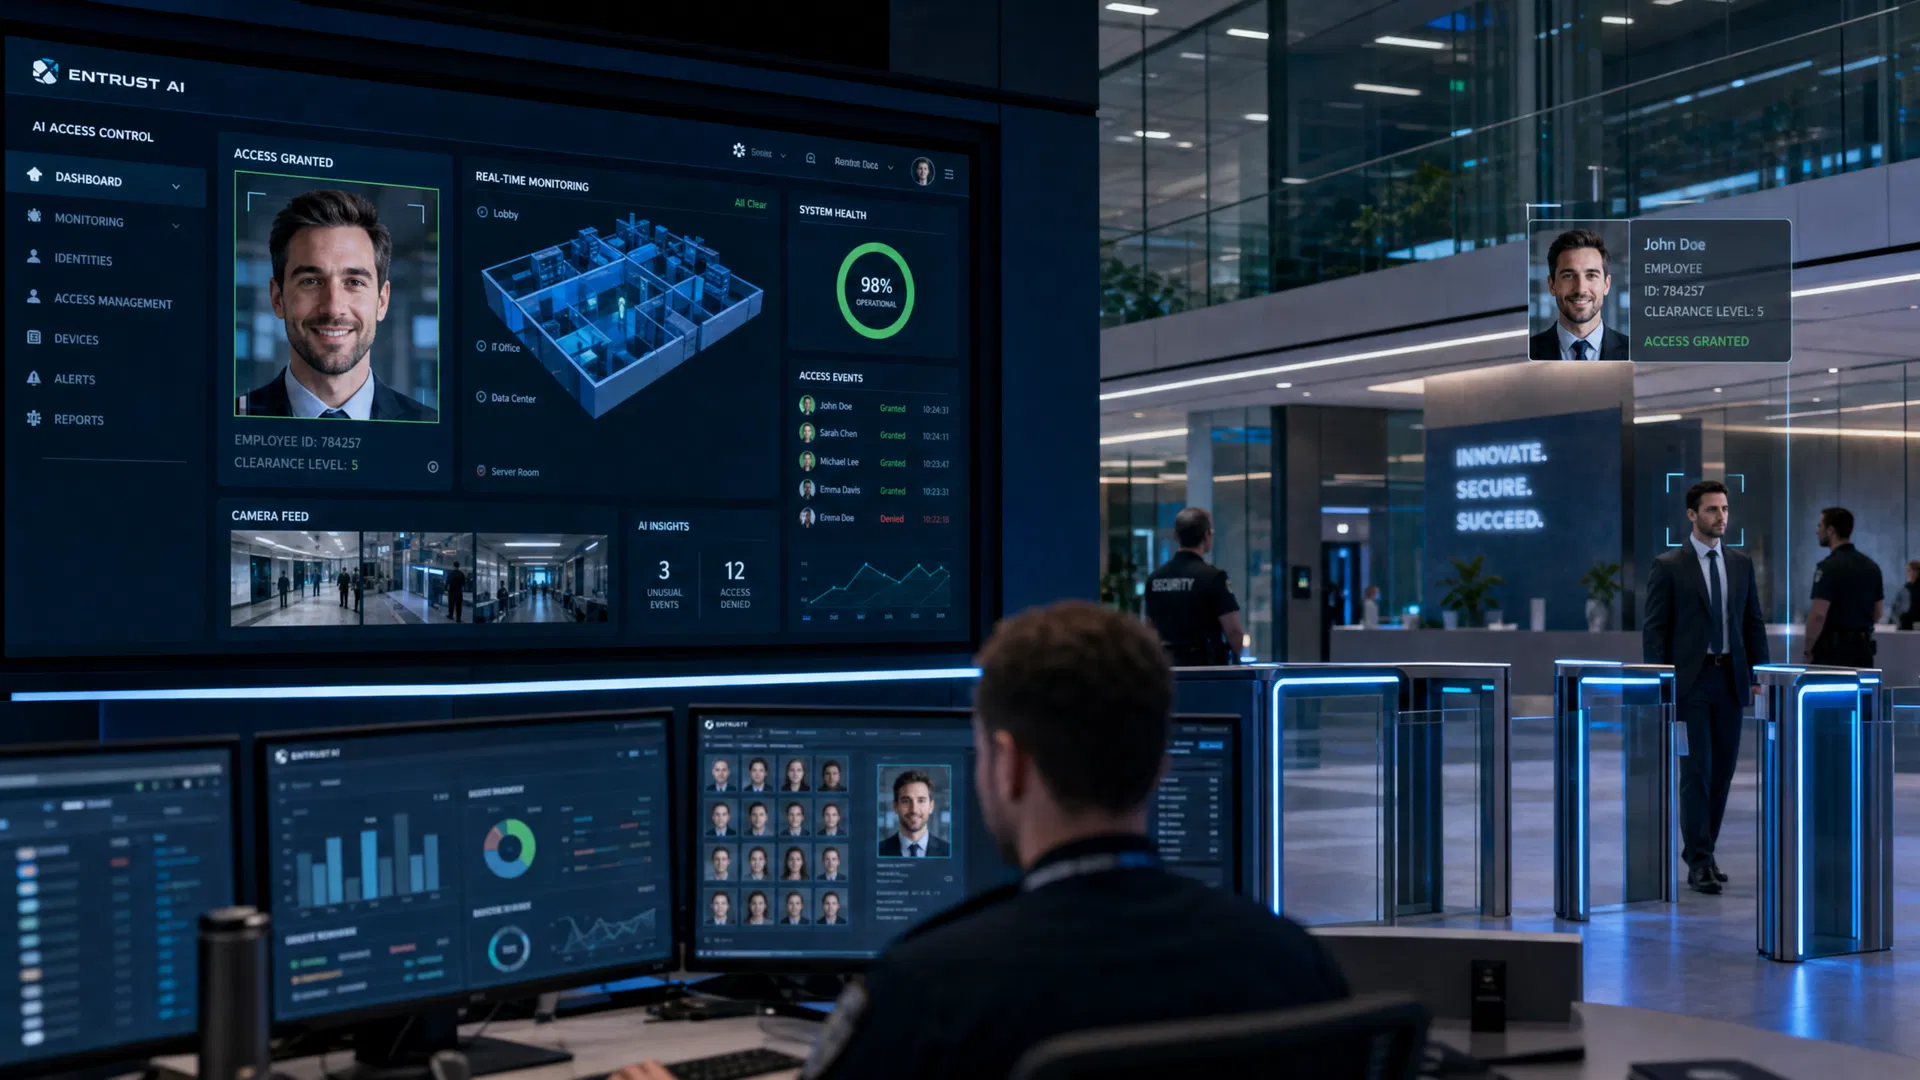
Most enterprise security programmes are designed around a binary model: authorised or not authorised, inside or outside. It is a model built for an era when organisations were simpler, workforce populations were stable, and the threat environment was less sophisticated. Modern enterprise security has to be more capable — managing complex populations, dynamic access requirements, and behavioural risk signals that static access control cannot detect. The shift from perimeter defence to risk intelligence is not optional; it is the direction the threat environment is forcing.
In our experience implementing enterprise access governance systems, the most immediate security finding in almost every organisation is credential hygiene — the gap between who officially has access and who actually needs it. In a government ministry assessed in 2025, more than 1,200 active credentials belonged to former employees, ended contractor engagements, or personnel who had transferred facilities. Each credential represented an authorised entry point to sensitive areas for individuals with no legitimate business being there. This problem is endemic in large organisations, and it is invisible until you look systematically.
Physical access intelligence becomes significantly more valuable when integrated with other enterprise systems. An access event at 02:00 that follows an after-hours digital access attempt from an unrecognised location tells a different security story than the same access event on a normal working day. Building the integrations that surface these context signals requires a security architecture that connects physical and digital security operations — and a platform designed from the start to handle that integration at enterprise scale.
Most enterprise AI programmes fail not because of the technology but because of how organisations approach them. The firms capturing lasting value share three disciplines that have nothing to do with model performance.
Telecom operators have invested heavily in network infrastructure. The returns on that investment are increasingly determined not by the infrastructure itself but by the intelligence layer running on top of it.
Governments and enterprises across the Gulf are committing significant capital to AI transformation. The organisations seeing results are those that treated AI as a strategic management question before treating it as a technology question.
Most organisations approach data architecture as an IT infrastructure question. The firms that extract the most business value from their data treat it as a strategic design question — one that belongs in the boardroom, not just the server room.
Financial institutions have been among the earliest and most enthusiastic adopters of AI. They have also produced some of the clearest illustrations of where AI programmes go wrong and what it takes to make them last.
Retailers collect more customer data than ever. Most of it sits in systems that don't talk to each other, analysed by teams that don't talk to merchants. The result is insight that arrives too late to matter.
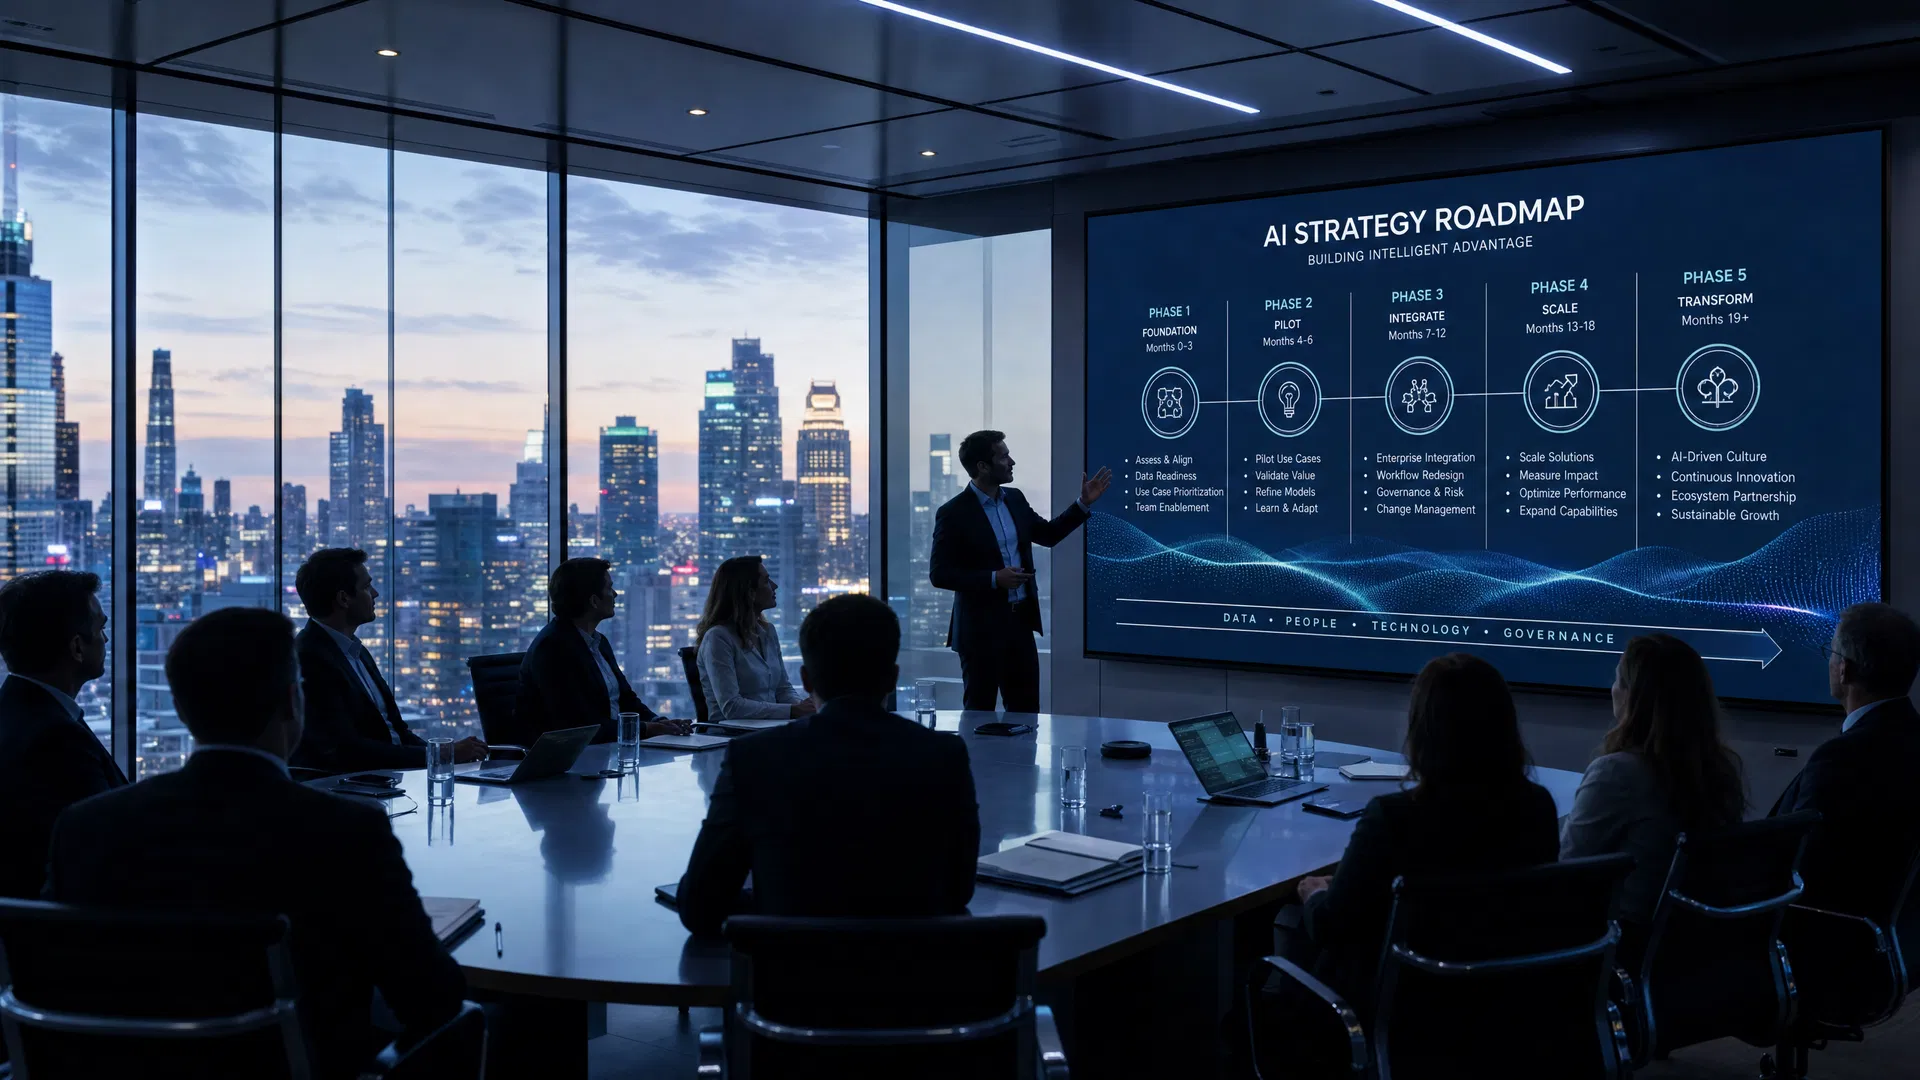
AI readiness is not a technology question. It is a diagnostic across strategy, data, governance, talent, and operating model. Most organisations that think they are ready are not — and the signals are detectable before any money is spent.
Healthcare AI projects fail at a rate that should give every executive pause. The failure mode is rarely the algorithm — it is the operating environment the algorithm is dropped into without adequate preparation.
Route optimisation is frequently the first AI application logistics companies pursue. It is also the one most likely to deliver disappointing results — not because the technology doesn't work, but because the problem definition was wrong from the start.
The energy transition story is usually told as a generation story. The harder problem — and the one operators are investing the most in — is grid flexibility: matching variable supply and variable demand in real time across infrastructure built for neither.
Smart city pilot projects are familiar. Smart city permanent operating capabilities are considerably rarer. The difference between cities that make the transition and those that do not comes down to a small number of decisions made at the start.
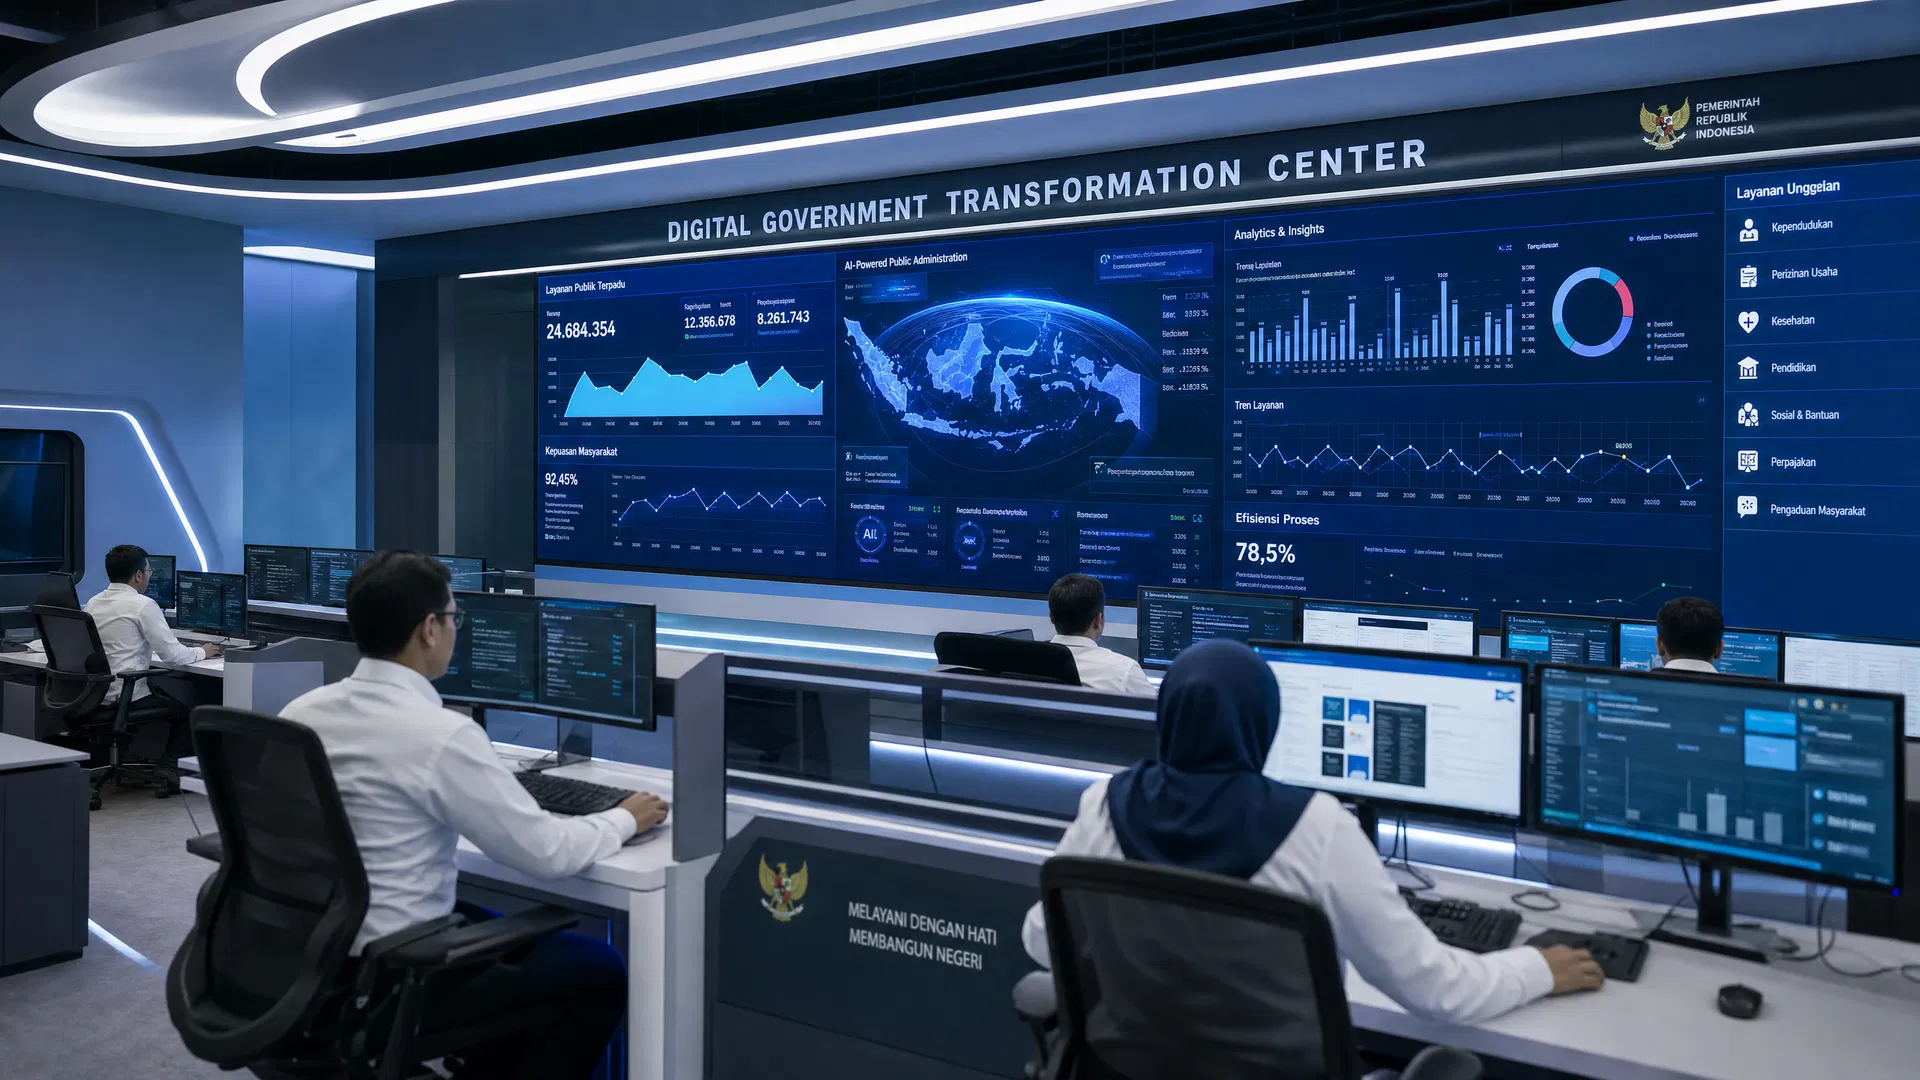
Government digital programmes report high levels of service digitisation. The metric that matters — end-to-end completion rate — tells a different story. Most programmes have not yet made the measurement straightforward enough to be honest about it.
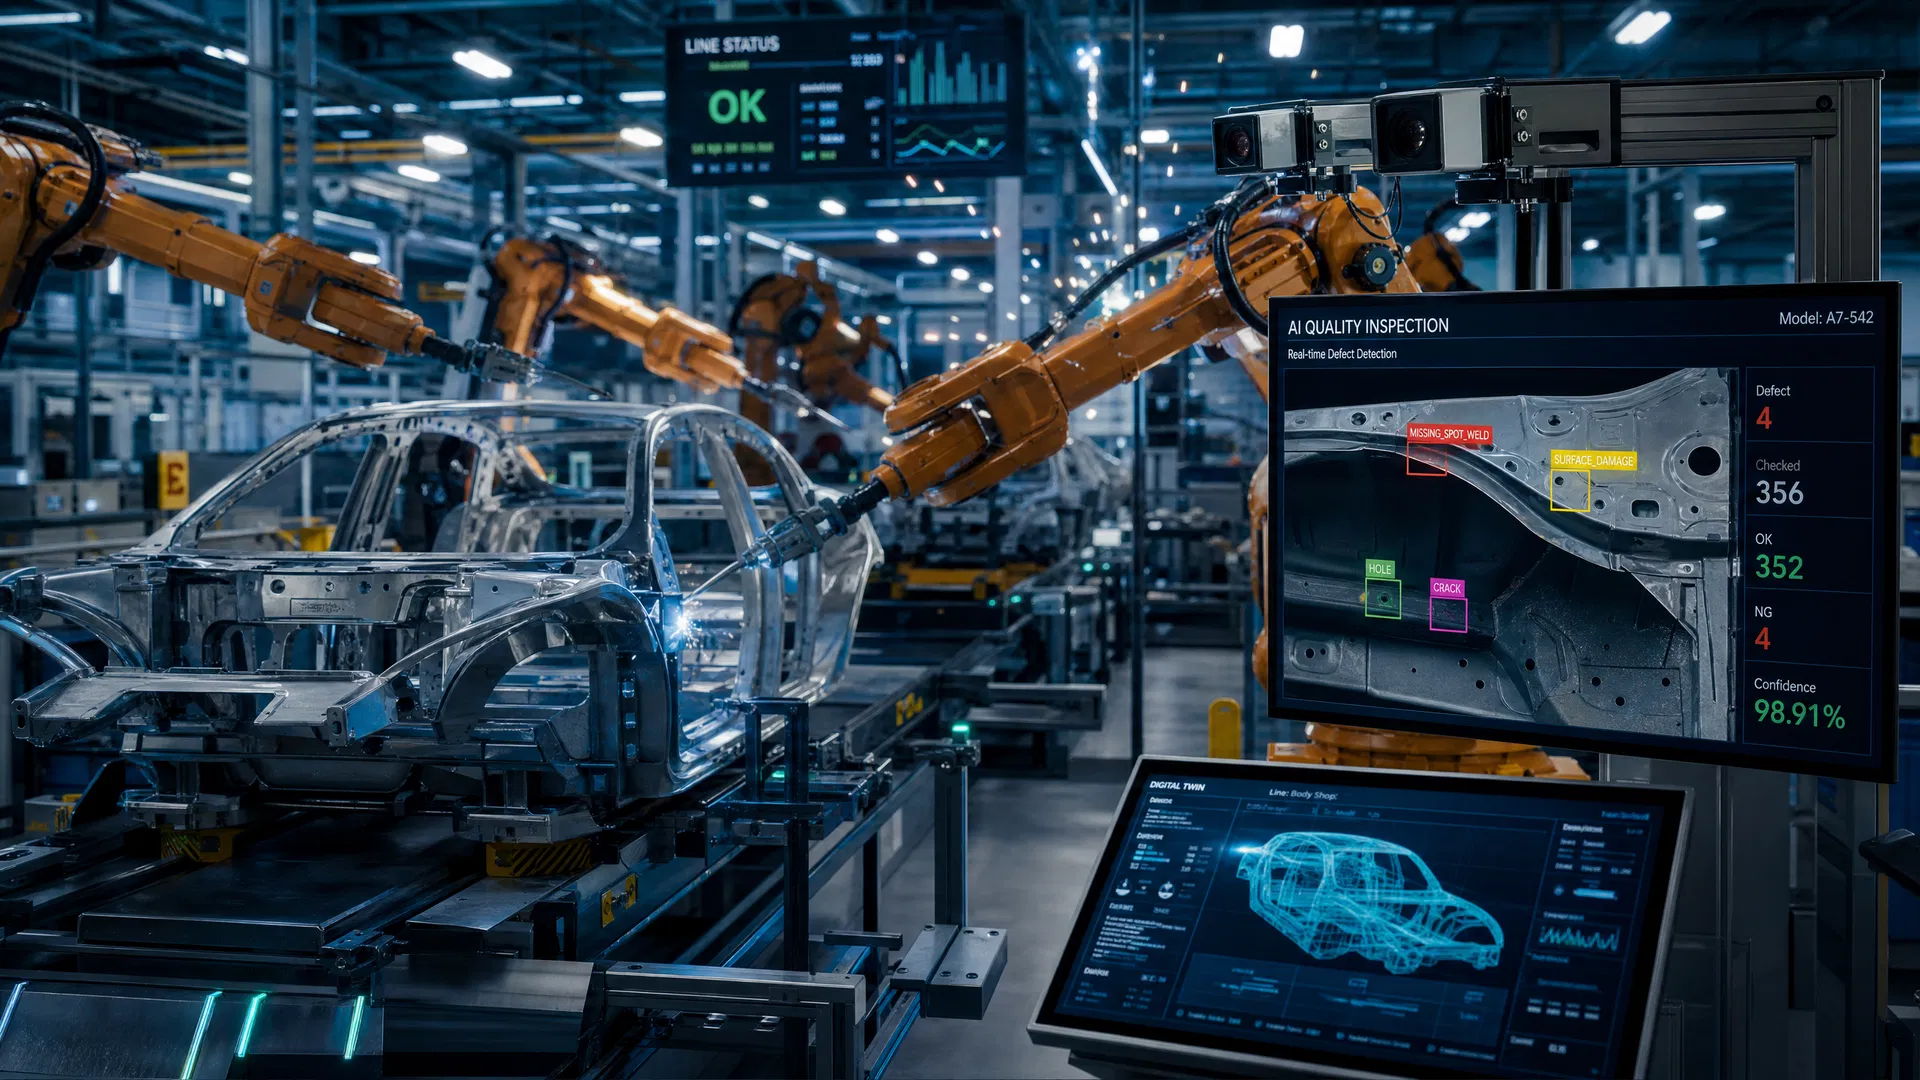
Real-time quality inspection technology has matured. The constraint on returns is no longer the model — it is the operating environment, the taxonomy, and the discipline to keep the system trustworthy through normal manufacturing variation.
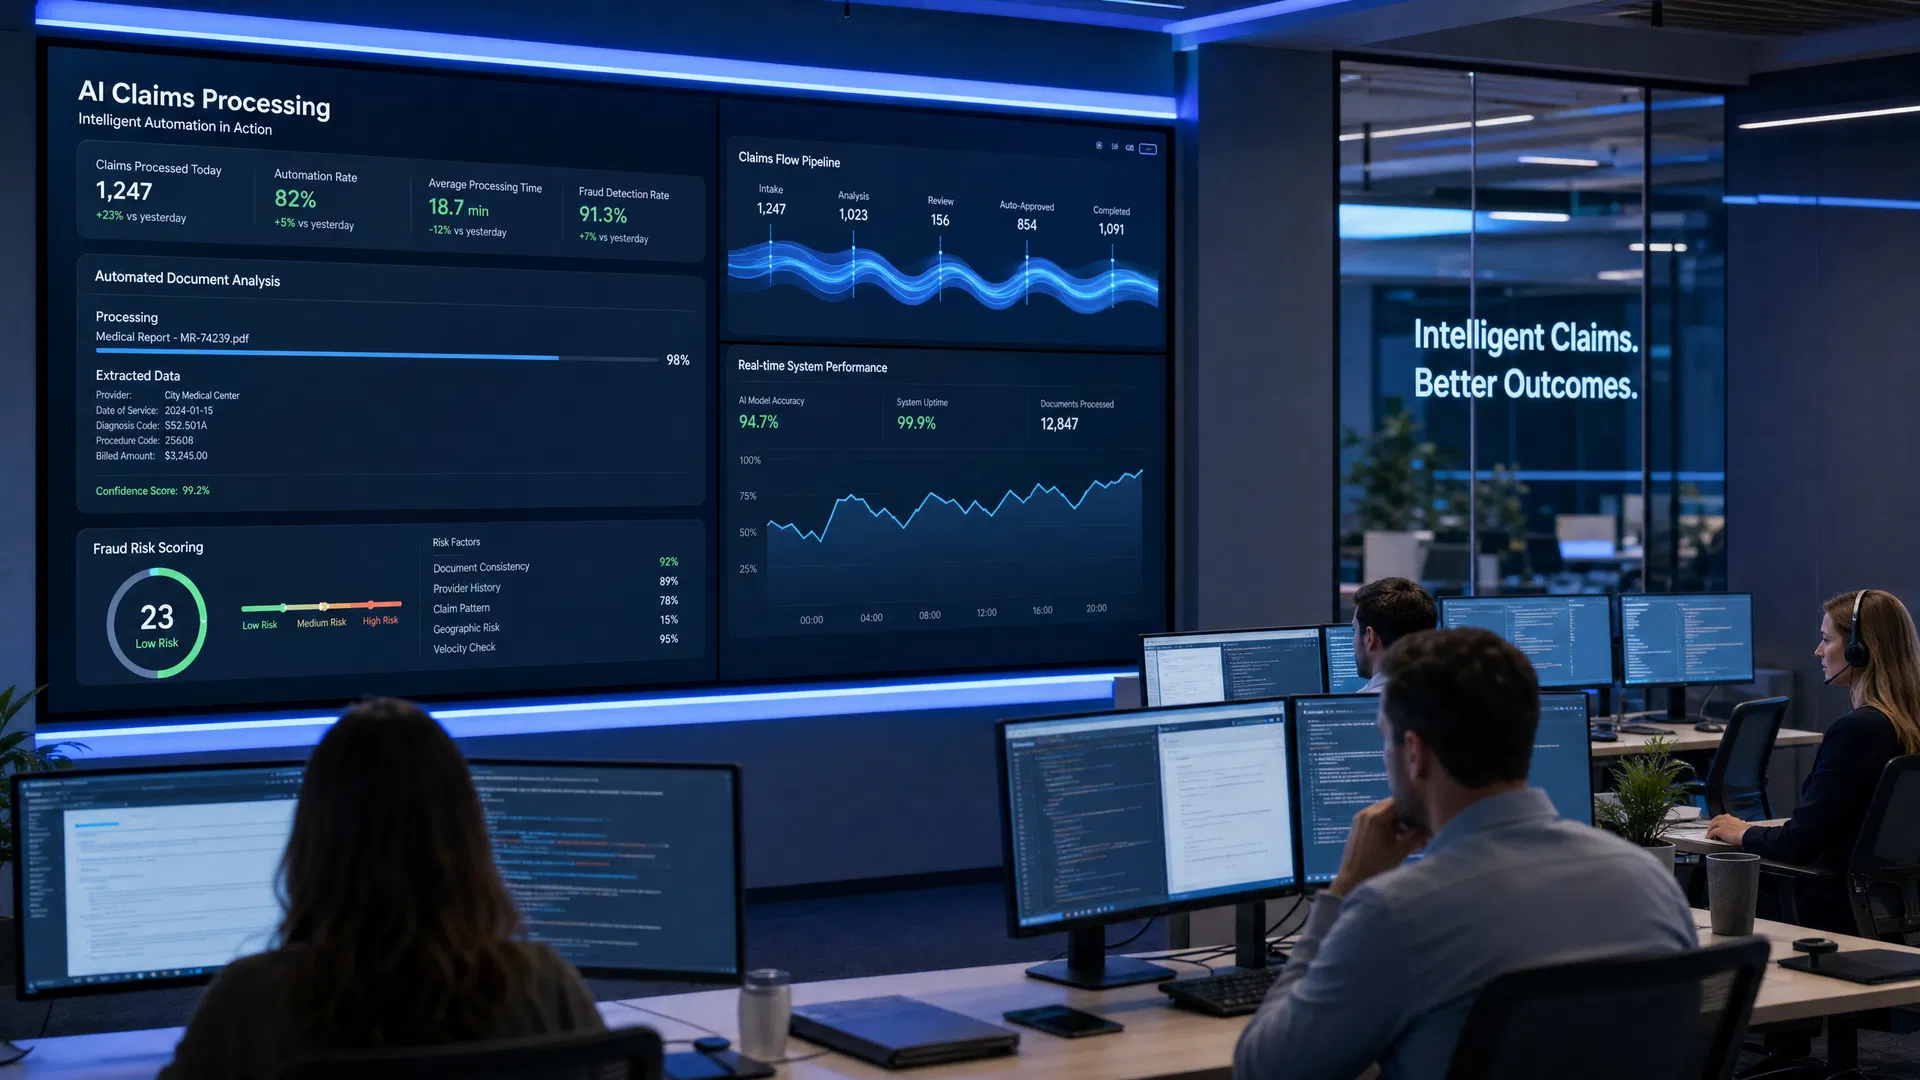
Claims automation has a sound business case. It also has a set of trade-offs that are routinely underweighted in the evaluation process. A candid note for insurance executives assessing the move.
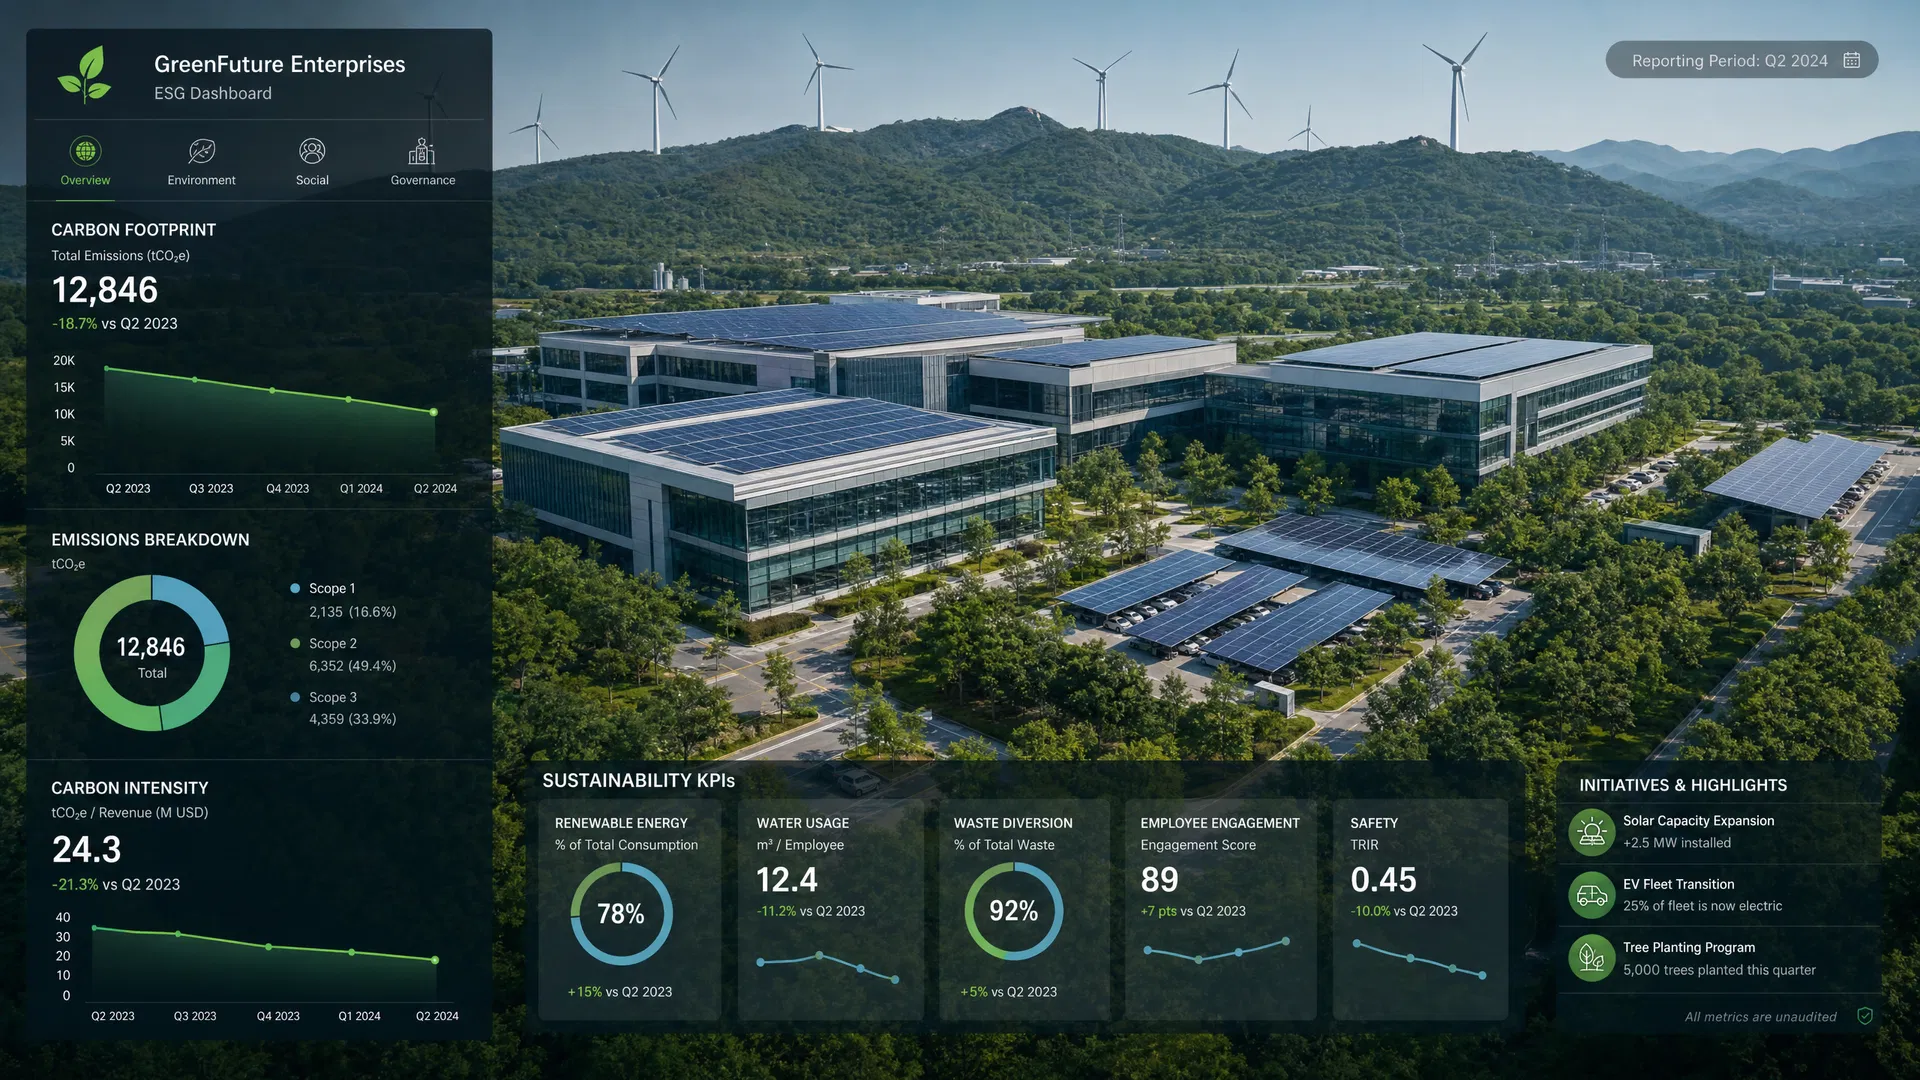
ESG reporting is moving from voluntary disclosure to assurance-grade obligation. Most enterprises are not ready, and the reason is rarely policy — it is the data layer underneath the report.
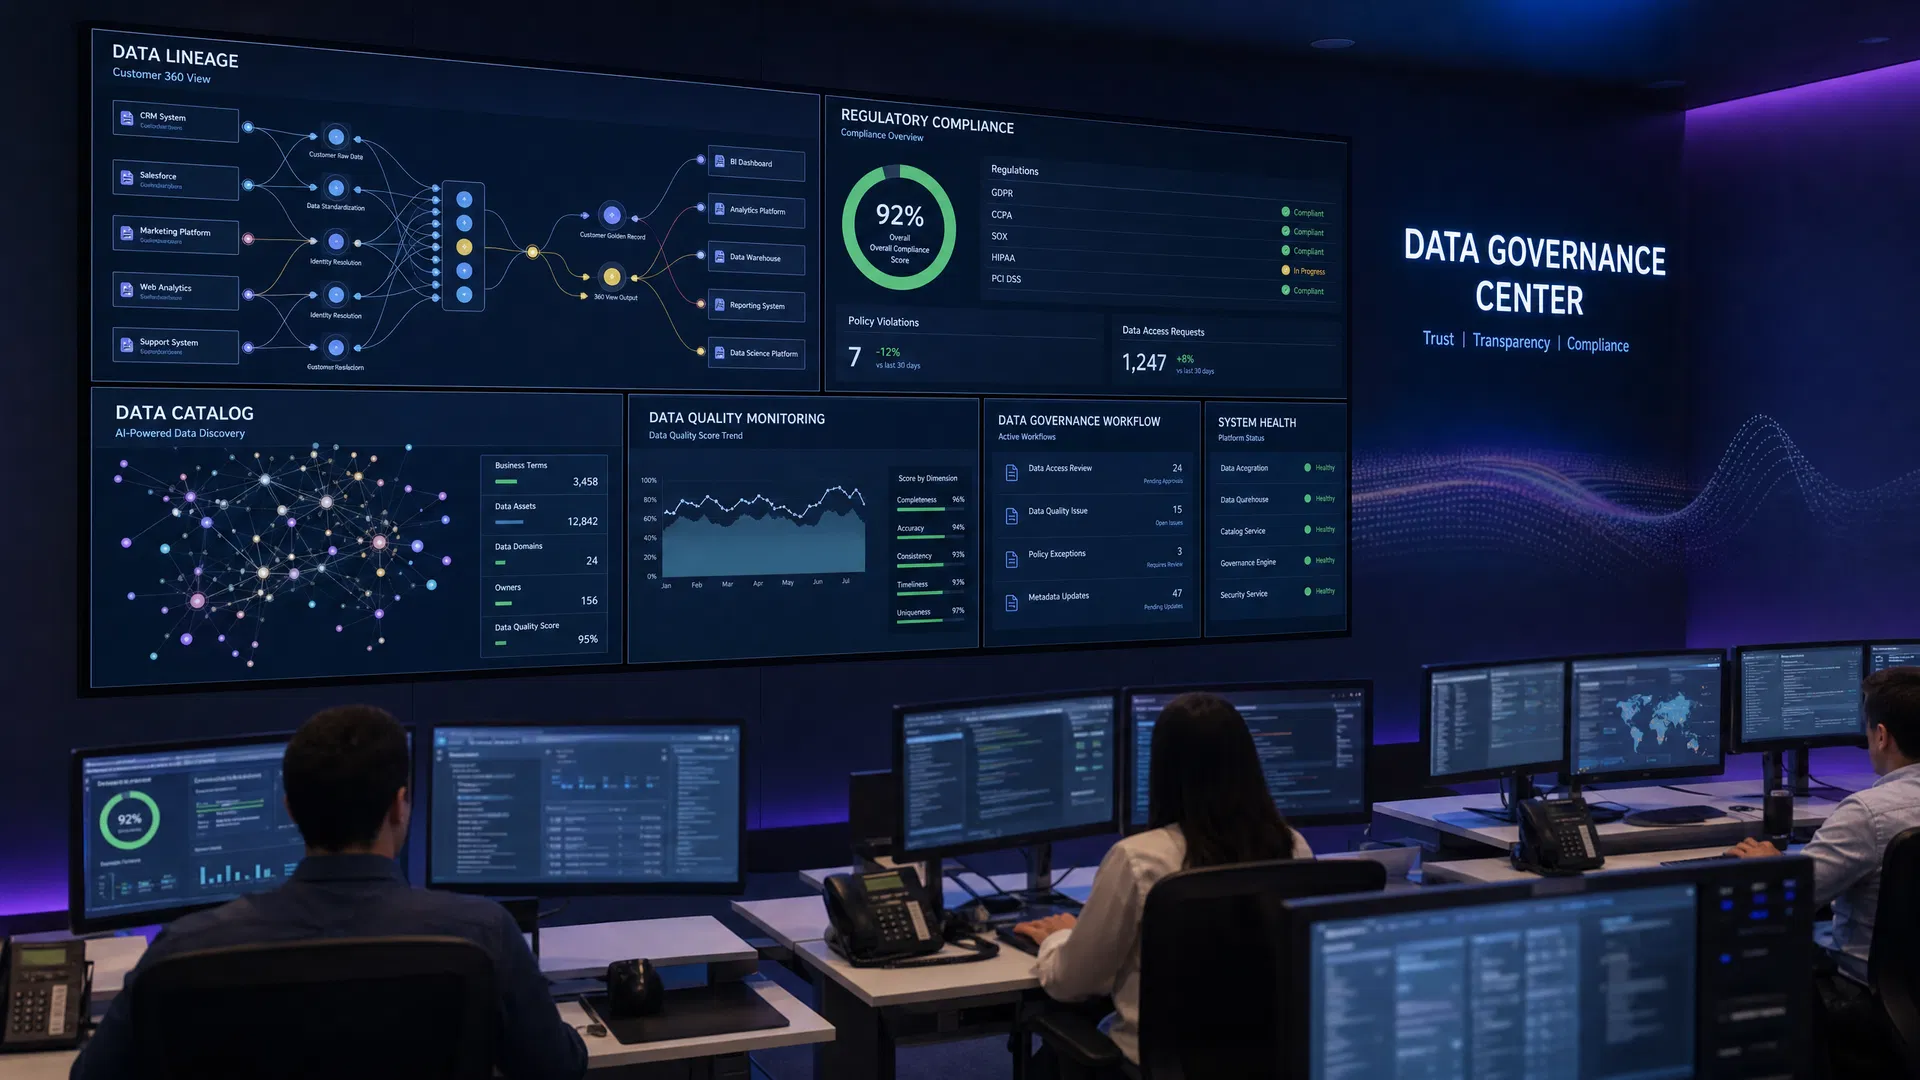
Data governance was a back-office concern until AI made every production model a regulated artefact. The four decisions that determine whether an enterprise's governance approach holds up under supervisory scrutiny.
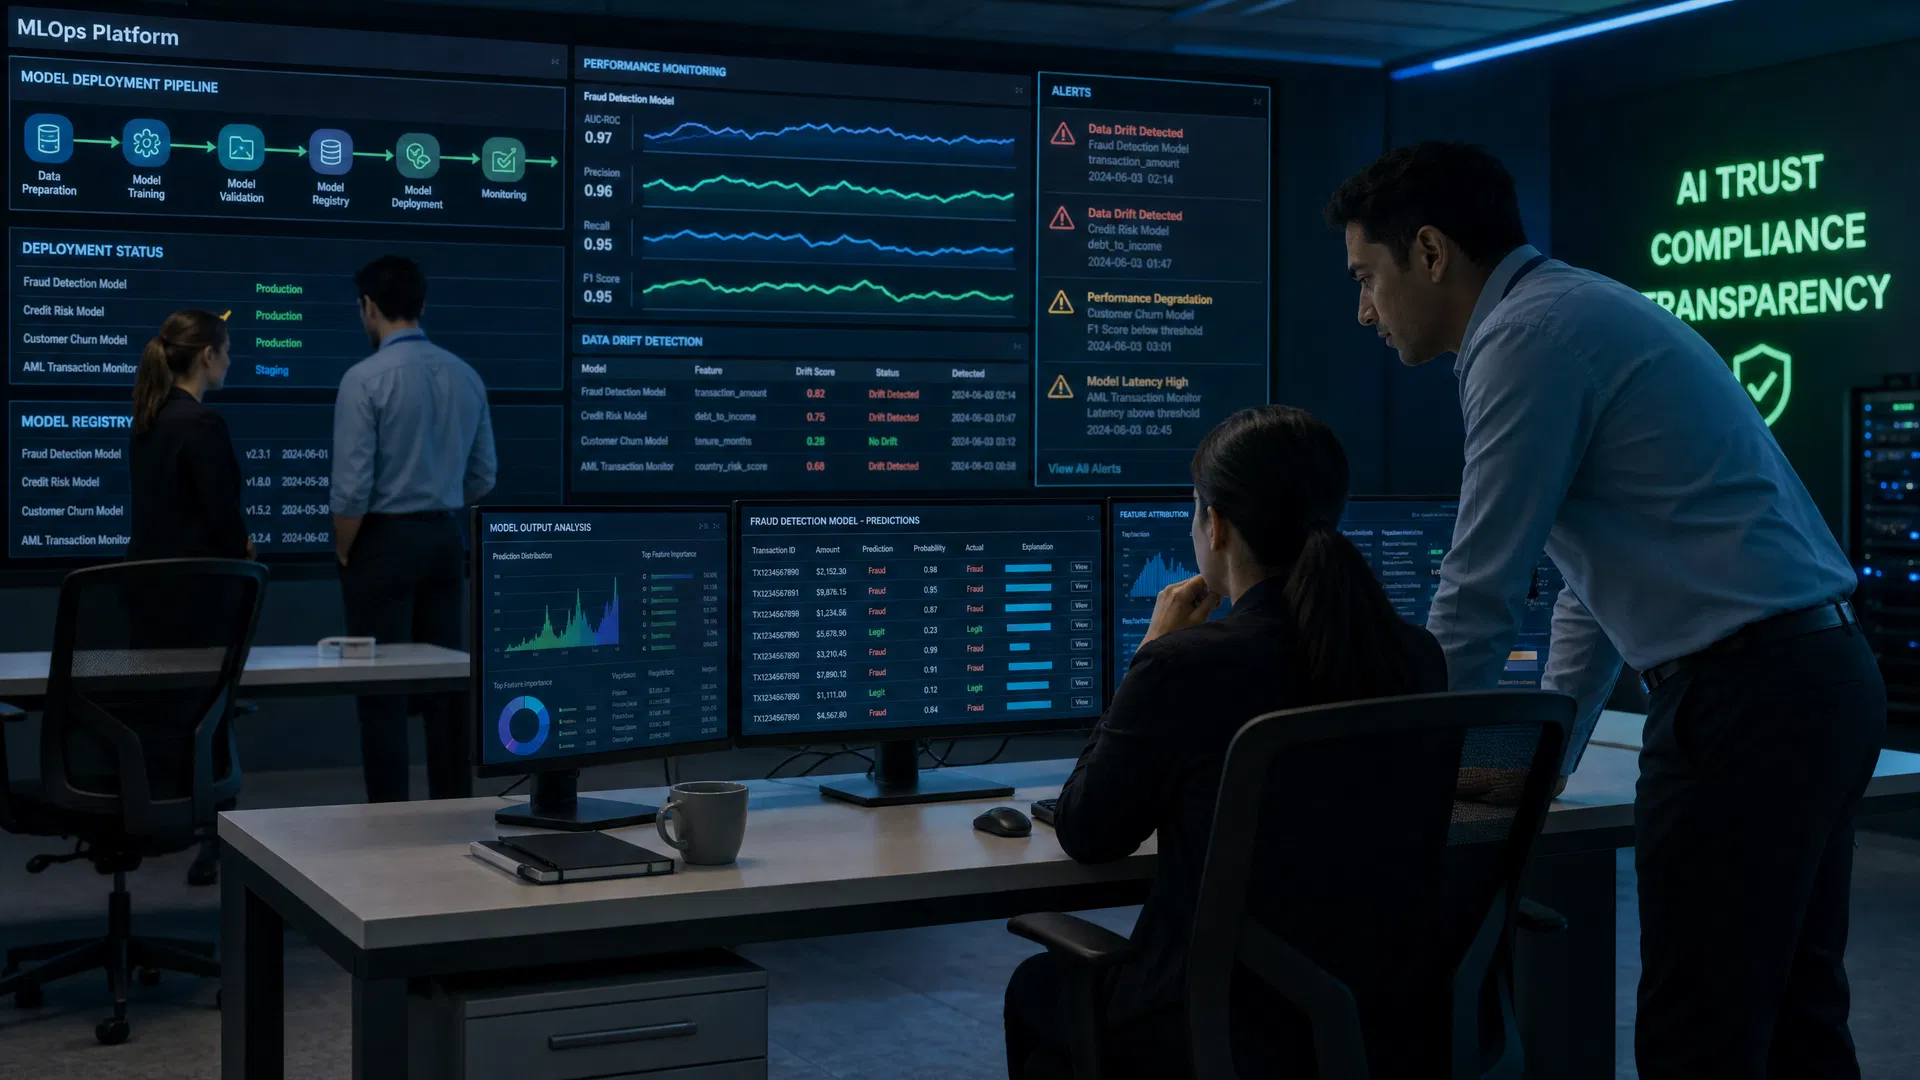
MLOps reference architectures are well documented. None of them describe what changes when the model is regulated and every promotion to production needs documented approval from a named accountable person.
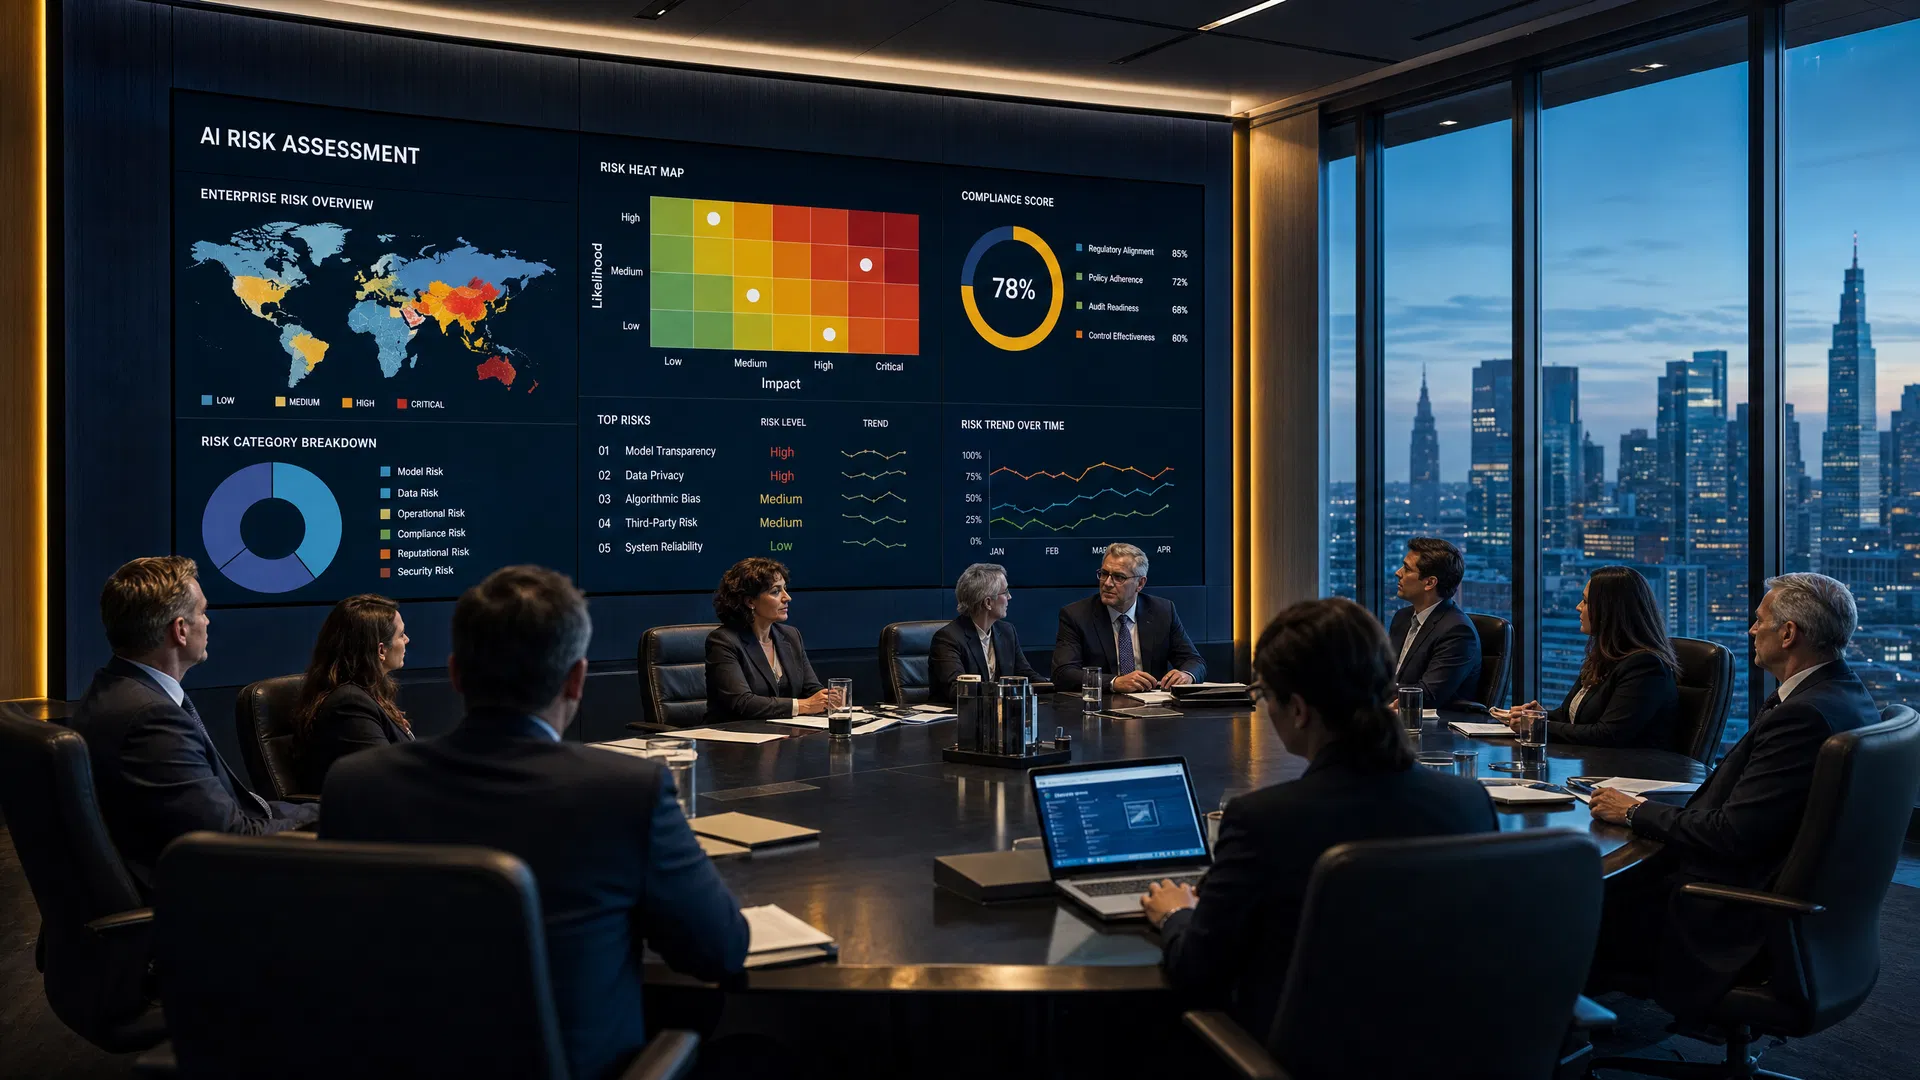
Boards have moved past asking whether the enterprise should use AI. The question is now what the enterprise is exposed to by using it, and whether management can demonstrate the answer is known and managed.
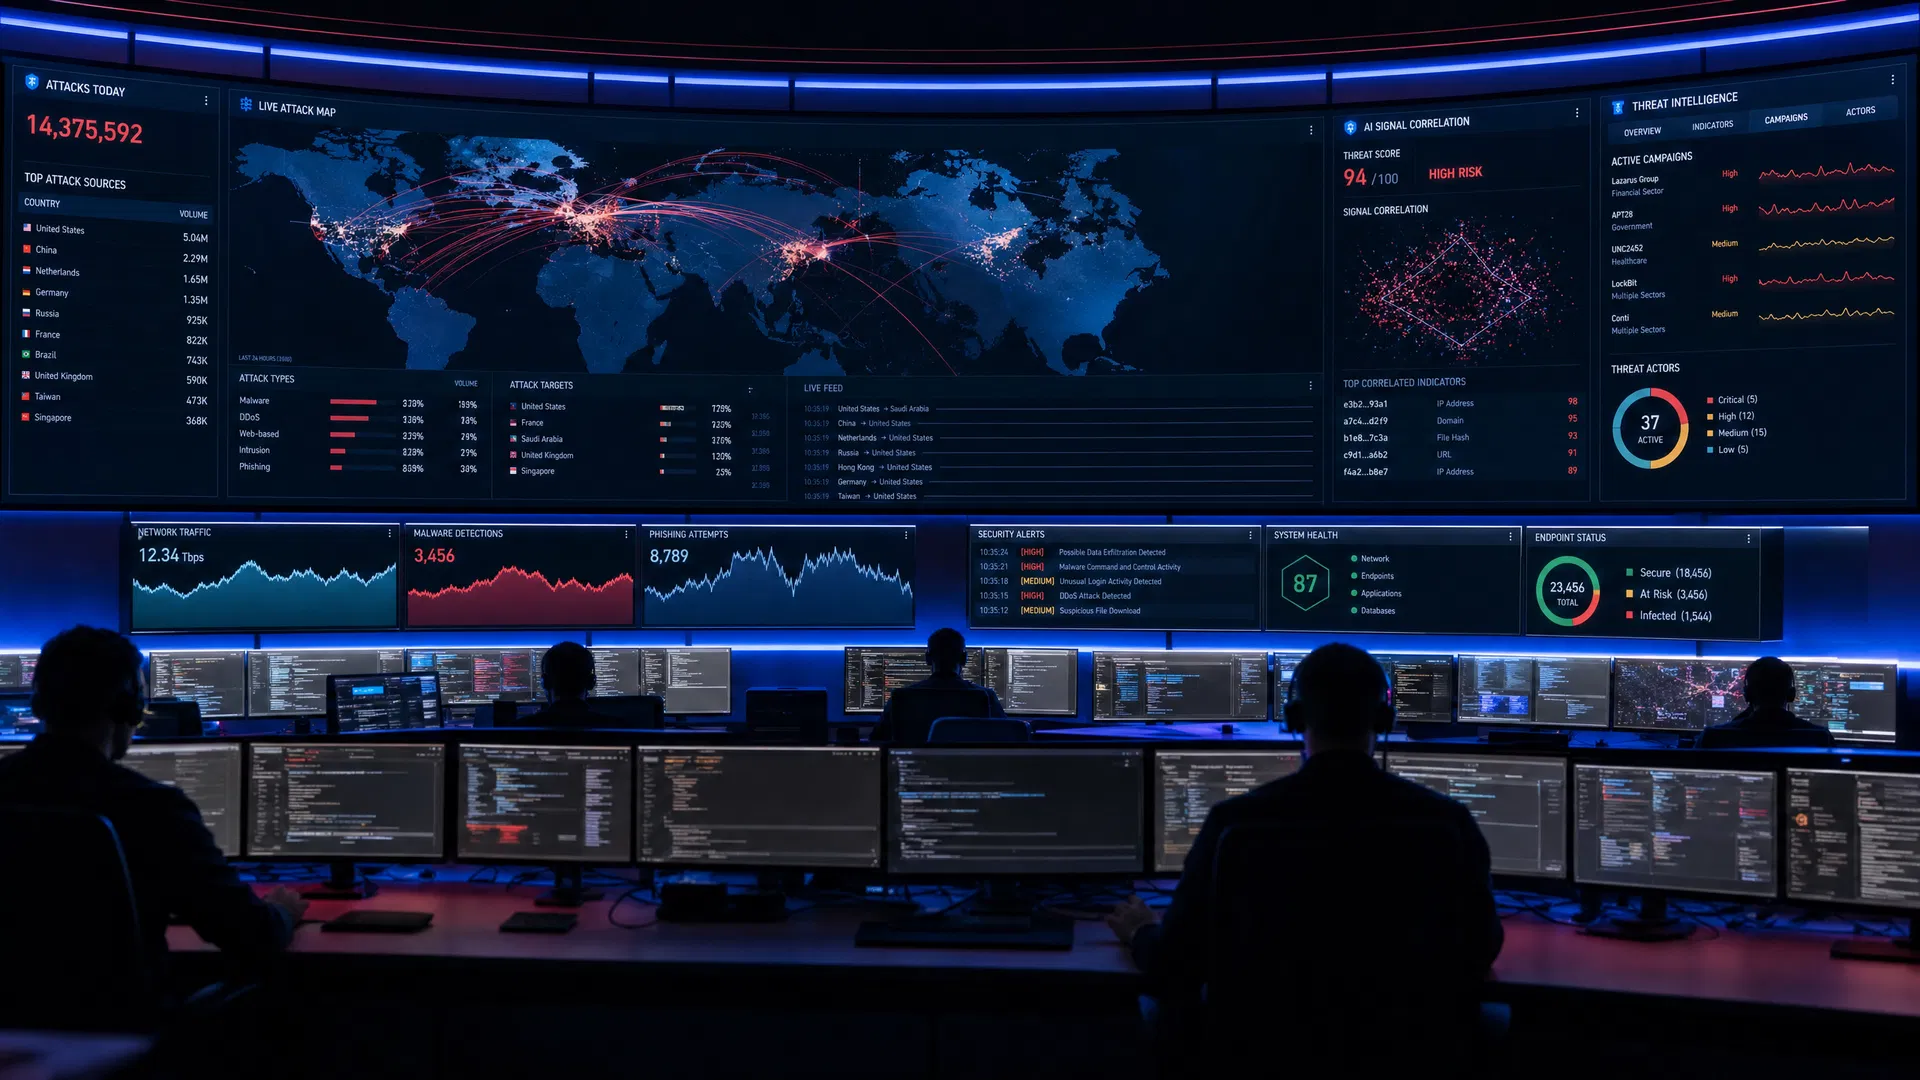
AI in the security operations centre tends to fall into one of two patterns: the kind that converts existing alert noise into actionable signal, and the kind that adds more noise. The distinction is detectable before you sign the contract.